Investing in Italy: A 2026 Legal Guide to M&A and Corporate Strategy

Navigating the Italian Market: Opportunities, Nuances, and Legal Excellence

Expanding into the Italian market requires more than just local knowledge, but it demands a comprehensive Legal Guide to M&A and Corporate Strategy tailored to the unique dynamics of the Mediterranean business landscape. As Italy evolves into a sophisticated hub for tech innovation and high-end manufacturing, foreign investors and international partners need a team that can bridge the gap between global goals and local regulations. At Princivalle Apruzzi Danielli, we act as your strategic bridge, aligning global business goals with the intricacies of Italian corporate law to ensure seamless transactions. Here is our short Legal Guide to M&A and Corporate Strategy

1. The Heart of Italy: Navigating the SME Ecosystem

The backbone of the Emilia Romagna’s and Bologna’s area economy, is its dense network of Small and Medium Enterprises (SMEs). For a foreign entity looking at M&A, this presents a unique set of challenges and opportunities:

  • Beyond the Balance Sheet: Many Italian targets are family-owned businesses with deep local roots. Successful acquisitions require navigating complex governance structures where personal trust and “soft skills” are often as critical as the financial valuation.

  • Cultural Integration in M&A: Managing the transition from a founder-led company to a structured corporate environment is a delicate legal and managerial process. At Princivalle Apruzzi Danielli, we ensure that the Sales and Purchase Agreement (SPA) accounts for these nuances, protecting the buyer’s interests while ensuring business continuity.

2. Commercial Contracts: Civil Law vs. Common Law

One of the biggest hurdles for foreign entities is the transition from Common Law logic to the Italian Civil Code. Whether it’s a distribution agreement or a complex supply contract, the “hidden” rules of good faith (buona fede) and statutory warranties can significantly alter the risk profile of a deal.

Pro Tip: Don’t just translate your standard international templates. Localizing a contract for the Italian jurisdiction isn’t a formality: it’s a risk mitigation strategy.

3. Why Global Firms Partner with Princivalle Apruzzi Danielli

International law firms often need a “boots on the ground” partner in Italy who speaks the same language—both literally and professionally. Our approach at Princivalle Apruzzi Danielli is defined by:

  • Efficiency: We strip away the bureaucracy to focus on deal-closing.

  • Directness: We provide clear “Go/No-Go” advice rather than 50-page theoretical memos.

  • Multidisciplinary Vision: From corporate restructuring to complex commercial litigation, we protect your interests at every stage of the business lifecycle.

Conclusion: Italy is Open for Business

Entering the Italian market is a strategic move that requires a blend of global vision and local precision. Whether you are a foreign corporation looking for an acquisition or a law firm seeking a reliable Italian desk, the right legal partner makes the difference between a stalled project and a successful expansion.


How Princivalle Apruzzi Danielli Can Assist You

Our team is ready to support your cross-border operations with tailored legal solutions.

Contact us at www.padlex.com to discuss your Italian strategy.

Business unit transfers in Italy: legal insights for International Groups

The Firm recently advised an Italian company, wholly owned by a foreign holding company, on a business unit transfers in Italy (ramo d’azienda) carried out as part of a broader corporate reorganisation.
The transaction highlights the importance of understanding Italian business transfer law when foreign companies operate in Italy and engage in carve-out or disposal transactions governed by Italian civil law.

Business Unit Transfers under Italian Law

Under Italian law, the transfer of a business or business unit is a statutory transaction with effects that extend well beyond a traditional asset sale.
A business unit transfer involves the transfer of an organised and functionally autonomous business capable of carrying out an economic activity on an independent basis.

As a general rule, a transfer of business in Italy includes:

  • tangible and intangible assets forming part of the business unit;

  • ongoing commercial contracts connected with the transferred activity;

  • employees assigned to the business unit, with automatic continuation of employment relationships;

  • rights and certain liabilities related to the operation of the business.

Correctly defining the perimeter of the business unit is therefore essential to ensure consistency between the commercial objectives of the transaction and its legal consequences under Italian law.

Key Challenges for Foreign Companies Operating in Italy

A central aspect of the transaction was assisting the foreign parent company in navigating the mandatory rules of Italian civil law, which often differ significantly from common law frameworks.

In particular, Italian business transfer law provides for a number of effects that apply automatically by operation of law, including:

  • the automatic transfer of certain contracts without the need for individual counterparty consent, subject to statutory exceptions;

  • limitations on the contractual allocation of liability, with residual joint liability of the transferor vis-à-vis certain third parties;

  • extensive employee protection rules triggered by the transfer of a business or business unit;

  • formal execution and registration requirements that affect enforceability and third-party effectiveness.

For international groups accustomed to a more contract-driven approach, these constraints require early legal assessment and careful transaction planning.

A Practical and Transaction-Focused Legal Approach

The Firm provided hands-on legal support throughout the entire carve-out process, focusing on execution efficiency and risk management. In particular, the Firm:

  • advised on the non-waivable effects of a business unit transfer under Italian law;

  • supported the client in structuring the transaction in line with group strategy;

  • coordinated with foreign legal advisors and internal corporate stakeholders;

  • drafted and negotiated transaction documents fully compliant with Italian civil law requirements.

This pragmatic approach enabled the client to complete the transaction smoothly while mitigating legal, operational and post-closing risks.

Supporting International Investors in Italian Transactions

The Firm regularly advises international groups, foreign investors and multinational corporations on:

  • transfers of business and business units in Italy;

  • carve-out transactions and corporate reorganisations;

  • cross-border M&A transactions governed by Italian law.

By combining strong technical expertise with a deep understanding of cross-border deal dynamics, the Firm acts as a reliable legal partner for foreign companies operating in Italy, translating business objectives into effective and compliant legal solutions.

For further information on business unit transfers in Italy or assistance with similar cross-border transactions, our team is available to support clients at every stage of the process.

Governing Law Clauses in International Contracts

A Practical Guide under Italian Law

In international contracts, the governing law clauses plays a crucial role. They determine which legal system will govern the agreement in case of disputes, performance issues, or interpretative doubts.

This article provides a short practical overview of how to draft and apply governing law clauses in international contracts involving Italy. We cover what qualifies as an international contract, the validity of the clause under Italian law, what happens when no law is chosen, and when the 1980 Vienna Convention (CISG) applies automatically.

What is an international contract?

A contract is considered international when it presents connections to more than one legal system. This may occur when:

  • the parties are based in different countries;

  • the place of performance differs from the place of conclusion;

  • the subject matter of the contract involves cross-border movement.

Even one international element is enough to trigger the application of Italian private international law (Law No. 218/1995) and EU Regulation Rome I (Reg. 593/2008).

Why a governing law clause is essential

Including a governing law clause offers key advantages:

  • Legal certainty in case of disputes;

  • Predictability of applicable rules for performance, interpretation and liability;

  • Avoidance of costly litigation over conflict-of-law issues;

  • Strategic leverage if the chosen law is that of the drafting party’s country.

Without this clause, courts will apply default conflict rules, which may lead to unexpected or less favourable outcomes.

Validity under Italian law

Under EU Regulation Rome I, parties are free to choose the law governing their contract, as long as:

  • the choice is clearly expressed, or

  • it is clearly implied from the terms of the contract or the circumstances.

Article 57 of Italian Law 218/1995 incorporates this principle even when the contract involves non-EU countries.

Mandatory limitations

However, certain rules prevail regardless of the parties’ choice:

  1. Overriding mandatory provisions of Italian or foreign law;

  2. Public policy (ordre public) of the forum State;

  3. Special protection rules for consumers, employees and insurance policyholders, which cannot be waived by contract.

How to draft effective governing law clauses

To ensure enforceability and clarity, use precise and complete wording. For example:

“This Agreement shall be governed by and construed in accordance with the laws of the Republic of Italy, excluding its conflict of law rules and the United Nations Convention on Contracts for the International Sale of Goods (CISG).”

Drafting tips:

  • Clearly specify the applicable law;

  • Indicate whether the CISG or other uniform laws are included or excluded;

  • Align the clause with any jurisdiction or arbitration provisions;

  • In multilingual contracts, define the prevailing version;

  • Consider a “static reference” clause (e.g. “laws as in force on the date of execution”) for legal certainty.

What happens if no law is chosen?

If the parties do not select a governing law, default rules under Rome I apply:

  • The applicable law shall be based upon the nature of the contract; or
  • The contract will be governed by the law of the country of the party performing the characteristic performance;

  • Exceptionally, the contract is governed by the law of the country with which it is most closely connected.

In all cases, the absence of a choice increases the risk of litigation and unpredictability.

When Italian law applies: beware of the CISG

If Italian law ends up governing the contract (either by choice or default), the United Nations Convention on Contracts for the International Sale of Goods (CISG) may automatically apply.

Italy is a signatory to the CISG, so it applies when:

  • the parties have their places of business in different CISG member countries;

  • the contract concerns the sale of goods (unless excluded).

To exclude the CISG, the parties must do so expressly, e.g.:

“This contract is governed by Italian law, with the exclusion of the CISG.”

If no exclusion is made, the CISG will apply by default — even if it is not mentioned.

Depending on the context, the CISG may benefit the seller (often the Italian party), but in certain industries or sectors, parties may prefer to rely on domestic law provisions instead.

Key recommendations

If you are drafting or negotiating a contract with a foreign counterpart:

  • Include a clear and valid governing law clause;

  • Coordinate it with jurisdiction or arbitration clauses;

  • Carefully evaluate whether to include or exclude the CISG;

  • If the applicable is the Italian law, identify and comply with any mandatory rules of Italian law (e.g. anti-bribery, sanctions, export control).

A well-drafted clause not only reduces legal risk — it also positions you for stronger, more efficient negotiation.

Conclusion

A governing law clause is not a formality — it’s a fundamental tool to manage risk, reduce cost, and ensure legal certainty in international transactions.

Our law firm regularly assists foreign companies and international law firms with contract drafting, review, and negotiation under Italian law. We provide legal advice in both Italian and English, with a focus on clarity, enforceability, and cross-border strategy.

Need help with a contract involving Italian law?

Contact us for an initial consultation — we’ll be happy to assist.

Disclaimer
The content of this article is provided for informational purposes only and does not constitute legal advice, nor does it establish an attorney-client relationship. While every effort has been made to ensure the accuracy of the information herein, laws and regulations may change, and their application may vary depending on specific circumstances. Readers are strongly advised to seek independent legal advice before making any decisions based on this content. For personalized legal assistance, please contact our firm directly.

Why Every Business Should Sign an NDA Before Sharing Confidential Information

What is an NDA?

A Non-Disclosure Agreement (NDA) is a legally binding contract under which one or more parties agree to keep certain shared information confidential. NDAs are often used in commercial negotiations, partnerships, investment discussions, or any situation where business-sensitive information is exchanged.

In short, an NDA protects your business know-how, data, strategies, and intellectual property from being disclosed or misused by others.


Why sign an NDA before sharing sensitive information?

In today’s competitive market, information can be more valuable than tangible assets. Whether you’re pitching to investors, discussing a new product with a supplier, or entering into a strategic partnership, the absence of a confidentiality agreement can leave your business exposed.

A well-drafted NDA helps:

  • Protect trade secrets and intellectual capital;

  • Set clear expectations and legal obligations;

  • Build trust between parties;

  • Deter misuse of proprietary information.


What does a standard NDA usually include?

While the structure may vary, most NDAs include several essential clauses:

1. Definition of “Confidential Information”

The agreement should clearly specify what qualifies as confidential — such as technical documents, financial data, business plans, software code, or any other proprietary materials.

2. Confidentiality Obligation

The receiving party agrees not to disclose, reproduce, or use the information except for the purposes outlined in the agreement.

3. Use Restrictions

The NDA should limit how the information can be accessed, stored, and shared — typically prohibiting unauthorised transmission or use.

4. Term of Confidentiality

Most NDAs remain in force for 2 to 5 years after disclosure, though some may stipulate indefinite obligations for particularly sensitive information (e.g. trade secrets).

5. Exceptions

Information that is already public, was known prior to signing, or is disclosed through legal means (e.g. court order) is typically excluded.


Useful but less common NDA clauses

Depending on the complexity of the deal or the industry involved, additional provisions may include:

  • Return or destruction of documents at the end of the relationship;

  • Non-solicitation or non-competition clauses;

  • Tracking of information shared digitally;

  • Specification of applicable law and jurisdiction, particularly important in cross-border relationships.


How long does an NDA last?

The duration can vary based on the nature of the business and the type of information disclosed. Generally:

  • During negotiations: confidentiality applies throughout the discussion period;

  • Post-termination: the NDA remains binding for a defined period (typically 2–5 years);

  • Unlimited: for certain types of intellectual property or trade secrets.


What are the risks of not signing an NDA?

Failing to execute an NDA can lead to:

  • Loss of control over your intellectual property;

  • Unauthorised disclosure or use of key business information;

  • Weakened legal position in case of disputes;

  • Potential financial and reputational damage.

In litigation, proving that information was meant to remain confidential becomes far more difficult without a written agreement.


NDA: A simple but essential legal safeguard

Whether you’re a startup founder or running an established company, using NDAs should be a standard practice when handling sensitive information. It is a low-cost, high-impact tool that safeguards your business interests.


Need an NDA tailored to your business?

There’s no such thing as a “one-size-fits-all” NDA. Each scenario demands a carefully drafted agreement aligned with the nature of the information and the specific context of the collaboration.

📩 Our law firm can help you draft or review NDAs that protect your assets and give you peace of mind. Get in touch for tailored legal advice.

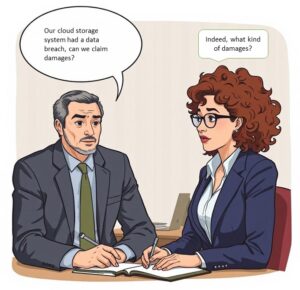
Claiming compensation for the data breach of a Cloud Storage System?

The use of cloud storage services has become a common practice, offering many advantages in terms of cybersecurity safeguard, scalability and accessibility. However, this choice does not imply the absence of significant risks, especially concerning the possible data breaches occurred to the provider.

In this article, we explore the kind of damages caused by a data breach suffered by a cloud storage provider, in accordance with the General Data Protection Regulation (GDPR), and the possibility of claiming compensation for the data breach.

Data breach under GDPR

Article 33 of the GDPR requires Data Controllers to notify the competent Supervisory Authority in the event of a data breach. A data breach can compromise the confidentiality, integrity, and availability of personal data, potentially leading to serious consequences for the affected individuals and the businesses involved.

When a data breach occurs, several parties can be involved: (a) The data subjects,  the individuals whose personal data has been compromised, including customers, suppliers, employees, and other individuals whose data was stored in the controller’s system, (b) the Data Controller,  the entity that determines the purposes and means of said personal data processing, (c) the Data Processor, the cloud service provider handling the personal data on behalf of the Data Controller.
Liability and damages

The GDPR clearly outlines the responsibility of both the Data Controller and the cloud service provider in a different and complementary manner. The controller is liable for damages caused by the breach of GDPR rules towards the data subjects, as specified in Article 82, paragraph 2, and Recital 146 of the GDPR.

On the other side, the cloud provider could be deemed liable for damages resulting from non-compliance with GDPR, absence of safeguards to protect the confidentiality of the information stored or infringment of the controller’s instructions, both towards the controller and the data subjects, as regulated by Article 1292 of the Italian Civil Code.

In most cases, it is assumed that the damage is attributable to the processor or a sub-processor, especially when the incident results from a failure to implement the security measures required by Article 32 of the GDPR.

To mention some examples, some years ago a serious incident occurred to a popular cloud provider in France hosting thousand of web sites and web platforms whose data center burnt in one night.  In a another case, whose lawsuit has been entrusted to Valentina Apruzzi, partner of Princivalle Apruzzi Danielli law firm, an unjustified disruption of data storage services by a cloud provider caused a serious data breach and related damages to our client.

The source and nature of the damages.

On one hand, contractual damages can be financial or non-financial, including reputational harm to the Data Controller. The provider may have failed to meet its obligations under the Data Protection Agreement (DPA) or to follow the controller’s instructions regarding the handling of personal data.

On the other hand, non-contractual damages, regulated under Article 82 of the GDPR, cover material and non-material harm, such as direct financial losses and moral damages. Therefore the Data Controller could be entitled to claim compensation for both kind of damages due to the data breach.

In the first mentioned case concerning the fire incident occurred to the clud provider, the decision of the Commercial Court of Lille in January 2023 marks a mainstone. The provider was ordered to compensate for damages, including loss of business goodwill, investment loss, reputational damage, and other related costs. Similarly, in another case, the Regional Court of Cologne recognized non-material damage to a data subject due to the controller’s failure to change access credentials, leading to a cyberattack.

Impact on the Data Controller

Data unavailability can cause significant disruption to day-to-day business operations, with serious financial impacts, including downtime costs and recovery expenses. Additionally, regulatory infringments can result in material fines, customer and partner’s trust may be severely damaged, leading to reputational harm. Businesses must also bear substantial costs to mitigate the damage and respond to the data breach.

For the data subjects, the unavailability of their personal data can lead to a loss of control over their information, limitations on their rights, discrimination, identity theft, or fraud, for instance. They may also experience financial losses. The unauthorized decryption of pseudonymized data can harm their reputation, and the loss of confidentiality in personal data protected by professional secrecy can have significant economic and social consequences.

Apologies can be considered a sufficient restore?

The decision of the Court of Justice of the European Union (CJEU) on 4 October 2024 concerning – among others issues -Article 82, paragraph 1, of the GDPR introduces a significant interpretation regarding compensation for claiming compensation for the data breach. It establishes that a formal apology may, in some cases, be considered an adequate remedy for such damage under the GDPR.

Here the key points of the decision:

  • The ruling clarifies that an apology can be viewed as sufficient compensation for non-material or intangible harm, such as emotional distress or reputational damage, under Article 82(1) GDPR. This reflects the court’s recognition of the nuances in addressing non-economic harm.
  • The court highlights that, in cases where it is impossible to fully restore the affected individual’s situation to what it was before the data breach or violation, other forms of compensation, like an apology, can be considered. This is especially relevant in scenarios where the harm caused cannot be undone by financial compensation alone.
  • The CJEU stresses that for an apology to be deemed adequate, it must be sufficient to compensate for the entire damage suffered. This means that the apology must provide real value in alleviating the harm experienced by the individual, addressing both the legal and emotional aspects of the damage.

This interpretation confirms and broadens the possible remedies available to individuals under the GDPR, beyond just financial compensation, allowing for more flexible and context-sensitive approaches to addressing data protection breaches.

For organisations found in breach of the GDPR, the ruling implies that non-monetary remedies, such as issuing a formal apology, may sometimes suffice, particularly in cases involving reputational damage or emotional distress. This could lead to a shift in how companies approach GDPR compliance and liability management.

While this ruling offers an alternative to financial compensation, it also raises questions about how the adequacy of an apology can be measured. Courts and regulators may face challenges in determining when an apology genuinely compensates for the damage suffered and when additional remedies are required.

In the case described above, where a provider suffers a data breach involving the personal data of a business entity claiming compensation for the data breach, we strongly doubt about the possibility to fairly restore the non tangible damages (such as the business reputation) claimed by the client by addressing him the most polite apologies.

Conclusion

To conclude, the unavailability of personal data caused by a breach of a cloud storage system can have devastating effects on both the Data Controller and the data subjects. As a result, it is crucial for businesses to adopt proactive measures to protect data and ensure business continuity in the event of a data breach. Recent court rulings, such as those from the Commercial Court of Lille and the Regional Court of Cologne, underscore the importance of a robust security strategy and regulatory compliance to mitigate the risks associated with data breaches.

International Legal Matters: Expertise in Assisting Clients Across Borders

International legal matters

International legal matters, such as those involving parties residing in different countries or property or assets located abroad, should never be underestimated or entrusted to those lacking the experience to fully understand and manage them effectively.

Businesses face the daily challenges of international markets, importing or exporting their goods and services.

Sometimes they need assistance in incorporating companies abroad or establishing a branch office in another country. That is why they increasingly seek competent professionals in this field.

Why Princivalle Apruzzi Danielli Law Firm

At Princivalle Apruzzi Danielli, an international law firm based in Bologna, Emilia Romagna, Italy, our team includes attorneys capable of providing legal assistance with:

  • drafting and negotiation of international contracts such as agency contracts, shares or property sale and purchase agreements, etc.
  • international litigation
  • setting up companies or branches in Italy or abroad
  • international debt recovery

When legal issues cross national borders, it’s essential to rely on professionals who can provide legal advice with expertise, precision, and speed. The factors to consider differ significantly depending on whether the legal matters are domestic or have international implications.

Moreover, our lawyers are fluent in English, ensuring that language is never a barrier when handling your legal needs.

Besides being all Italian qualified lawyers – avvocati – some of our attorneys are dual qualified lawyers, being qualified as solicitors for the jurisdiction of England and Wales (non-practising).

Our international clients

Whether you are an individual entrepreneur, a startup, or an established business in sectors such as services, manufacturing, IT, or e-commerce, you can rely on our experienced professionals to provide comprehensive legal support.

Additionally, we offer full legal assistance from Italy to foreign law firms needing support for their clients in our country, ensuring seamless collaboration across borders.

Is your e-commerce compliant with the Omnibus Directive?

Omnibus Directive protects consumers rights in online purchases

With the entry into force of Legislative Decree no. 26 of March 7, 2023, known as the “Omnibus Decree,” Italy transposed Directive Omnibus (EU) 2019/2161 of November 27, 2019. Such decree introduced significant amendments to the Italian Consumer Code (Legislative Decree no. 206/2005) to ensure a better  protection to consumers in online purchases.

How to fairly communicate price reductions in the web shops?

One of the most significant innovations concerns transparency in communicating discounted prices. According to Article 17 bis, para. 1 of the Italian Consumer Code, as amended by the Omnibus Decree, professionals must indicate not only the percentage discount but also the lowest price applied in the thirty days preceding the reduction. This provision aims to provide consumers with clear and complete information about the true benefits offered by promotions.

However, exceptions are provided for perishable food products to avoid excessive complexity in commercial communications concerning such products.

Fighting unfair competition practices and online reviews

The  European Omnibus Directive has introduced new provisions to fight deceptive commercial practices. Among these is the regulation of “Dual Quality,” which prohibits the promotion of goods as identical if there are significant differences between them in composition and characteristics.

Furthermore, stricter rules have been established for managing online reviews. As a consequence, it is now mandatory to indicate whether reviews come from consumers who have actually purchased the product, and sellers must take measures to verify the authenticity of such reviews.

Finally, the decree introduces harmonized sanctions at the European level for unfair commercial practices, ensuring greater uniformity in the application of sanctions among the Member States of the European Union.

On one hand the Omnibus Directive protects consumers online purchases, on the other hand it imposes the adoption of fair communications in order to push the e-commerce market.

Harmonized monetary sanctions

Monetary sanctions have been harmonized at the European level, with an increase in the maximum fine up to 10 million euros for violations of unfair commercial practices.

The sanctions are calculated considering various parameters, such as the nature and seriousness of the violation, the efforts of the professional to remedy the damage, and previous infringements.

Moreover, greater protections for consumers have been introduced, including the possibility of recourse to the ordinary judge to obtain proportionate and effective remedies in case of injuries suffered, such as compensation for damages or contract termination.

In conclusion, the Omnibus Decree represents a significant step forward in protecting consumers in online purchases, introducing clearer and stricter rules to counter unfair commercial practices and ensure greater transparency and fairness in the relationships between sellers and buyers.

Impact and compliance of the metadata collection by employers through email applications

Introduction

On December 21, 2023, the Italian Data Protection Authority issued a provision with significant implications for employers using email applications to manage internal communications. This provision focuses on the collection and retention of metadata relating to employees’ email accounts. In this article, we will examine the impact of this provision and the compliance requirements imposed on employers to adhere to said provisions.

What are metadata?

Metadata are data that provide information about the characteristics of other information. In other words, they are descriptions or additional information that provide context or structure to the main data. Here are some examples of metadata in different contexts:

  • Email Metadata: In emails, metadata includes information such as the sender, recipient, subject, date and time sent, transmission path, and other technical information that helps manage and organize emails.
  • Photo Metadata: For digital photos, metadata can include the date and time of capture, camera settings, GPS coordinates of where the photo was taken, and other information about the camera and shooting conditions.
  • Document Metadata: In digital documents, metadata can include information such as the document author, creation date, last modification date, document title, and other formatting and structure-related information.
  • Audio/Video File Metadata: In digital audio and video files, metadata can include information such as the song title, artist, album, year of release, duration, file format, and other recording-related information.

Metadata can be useful because it allows for the organization, search, retrieval, and better understanding of the main data. It can be used for various purposes such as digital content management, information retrieval, cybersecurity, regulatory compliance, and more. However, it is also important to consider privacy and security implications when managing metadata, as it can contain sensitive or confidential information.

Impact of the Authority’s guidance on metadata collection by employers

The Authority’s provision highlighted the risk associated with the preventive and generalized collection of metadata from email applications used by employees. Such metadata includes information such as sender, recipient, subject, date, and email size. The primary concern is that some computer programs and services may collect this metadata by default, without the employer’s ability to disable this functionality or limit the period of information retention.

Required Compliance

In response to this risk, the Data Protection Authority has mandated employers to adopt certain compliance measures to ensure compliance with privacy regulations and the protection of employees’ personal data. The following are the main compliance requirements:

  • Verification of Metadata Collection: Employers must diligently verify whether the computer programs and services used for email management collect metadata from employees’ accounts. This verification must be thoroughly documented to demonstrate compliance with the provisions of the provision.
  • Modification of Basic Settings: In case metadata collection is confirmed, employers must be able to modify the basic settings of computer programs and services to prevent the collection of metadata or limit the retention period to a maximum of 7 days, save the possibility of extending this period by an additional 48 hours in exceptional cases.
  • Labor safegards: If limiting metadata is not possible due to proven organizational or productive needs, employers must follow some safeguard procedures provided by sector regulations. This may include entering into a labour agreement with unions or obtaining authorization from the labor inspectorate. The aim is to ensure that extending the metadata retention period does not result in remote monitoring of employees’ activities.
  • Employee Information: It remains essential to provide employees with correct information regarding the processing of their personal data, including the collection and retention of metadata related to email.

Practical advice for metadata collection by employers

The Data Protection Authority’s provision represents a significant step forward in protecting employees’ privacy and regulating the use of metadata by employers. It is crucial for employers to take appropriate measures to comply with the established provisions while ensuring transparency and respecting employees’ rights.

Check of metadata collection, modification of email program settings, and adherence to labor safeguard procedures are essential steps to ensure compliance and mitigate risks associated with the management of employees’ personal data.


Italian companies’ law: division by separation

Transposition of the Directive (EU) 2019/2121 in Italy

Italy has recently transposed the Directive (EU) 2019/2121 of 27 November 2019 (amending Directive (EU) 2017/1132 as regards cross-border conversions, mergers and divisions), setting forth, inter alia, the rules governing the division by separation (scissione mediante scorporo).

Forms of company division available before the transposition

Until the transposition of Directive (EU) 2019/2121, the Italian law regulated only two kinds of company division:

  • Full division
  • Partial division

In case of a full division (scissione totale), a company, on – usually – being dissolved without going into liquidation, transfers all its assets and liabilities to two or more recipient companies, in exchange for the issue to the members of the company being divided of securities or shares in the recipient companies.

In case of a partial division (scissione parziale), a company transfers part of its assets and liabilities to one or more recipient companies, in exchange for the issue to the members of the company being divided of securities or shares in the recipient companies, and, under certain circumstances, in the company being divided or in both the recipient companies and the company being divided.

Division by separation

When a division by separation (scissione mediante scorporo) occurs, a company being divided transfers part of its assets and liabilities to one or more newly formed recipient companies, in exchange for the issue to the company being divided of securities or shares in the recipient companies.

More in details, the new rules have been enacted by implementing the Italian Civil Code with article 2506.1, headed ‘Scissione mediante scorporo’.

Furthermore, it has been discussed whether the company being divided can assign all of its assets and liabilities to the recipient company(ies). The prevalent opinion is that only part of the assets and liabilities can be assigned, thus sticking to the literal meaning of article 2506.1: if all the assets and liabilities were transferred, the transaction should be considered a contribution in kind (conferimento).

In addition, it is important to note that recipient company(ies) have to be newly formed and cannot pre-exist the division.

ENISA’s Data Processing Risk Analysis Method

Data processing is a critical aspect of business operations in the digital age. Protecting sensitive information and ensuring data privacy is of paramount importance. The European Union Agency for Cybersecurity (ENISA) offers a comprehensive risk analysis method to help organizations assess and manage data processing risks. Hereby we will describe the ENISA’s approach and explain how it can be a valuable tool for safeguarding data.

What is ENISA?

ENISA, the European Union Agency for Cybersecurity, plays a pivotal role in enhancing the overall cybersecurity posture of EU member states. One of their key contributions is the development of guidelines and methodologies for various aspects of cybersecurity, including data protection.

ENISA’s Data Processing Risk Analysis Method

ENISA’s method for analyzing data processing risks is a structured approach designed to help organizations understand the threats and vulnerabilities associated with their data processing activities. It consists of the following key steps:

Data Mapping:

Identify and document the types of data your organization processes.
Determine where the data is stored, how it’s collected, and who has access to it.

Risk Assessment:

Assess the potential risks and threats that could impact the confidentiality, integrity, and availability of the data (CIA). Consider factors such as data breaches, unauthorized access, data loss, and compliance infringements.

Risk Identification:

Identify vulnerabilities in your data processing systems.
Pinpoint external threats and internal risks, such as human error or technical failures.

Risk Evaluation:

Evaluate the potential impact and likelihood of each risk.
Prioritize risks based on their significance and potential consequences.

Risk Mitigation:

Develop and implement security measures to reduce the identified risks.
This may include encryption, access controls, regular audits, and employee training.

Continuous Monitoring:

Regularly monitor your data processing activities and risk mitigation measures.
Adapt and update your risk analysis as new threats emerge or the business environment changes.

Reasons to use ENISA’s Data Processing Risk Analysis Method

ENISA’s approach is invaluable for several reasons.

Legal Compliance: It helps organizations comply with the EU’s General Data Protection Regulation (GDPR) and other data protection laws.

Proactive Risk Management: By identifying and mitigating risks in advance, organizations can prevent data breaches and costly legal consequences.

Enhanced Data Security: The method ensures data is stored and processed securely, protecting both the organization and its data subjects.

Data subject trust: By taking data protection seriously, organizations can build a strong relationship based on trust with their customers and partners.

Conclusion

ENISA’s data processing risk analysis method is a valuable tool for small and medium size organizations seeking to protect sensitive information and comply with data protection regulations. By following this structured approach, businesses can systematically identify and mitigate data processing risks, ensuring the security and privacy of the data they handle. In an era where data is a critical asset, ENISA’s methodology is a proactive step towards safeguarding it.